Wisp

Credentials
Secrets stay in the Keychain.
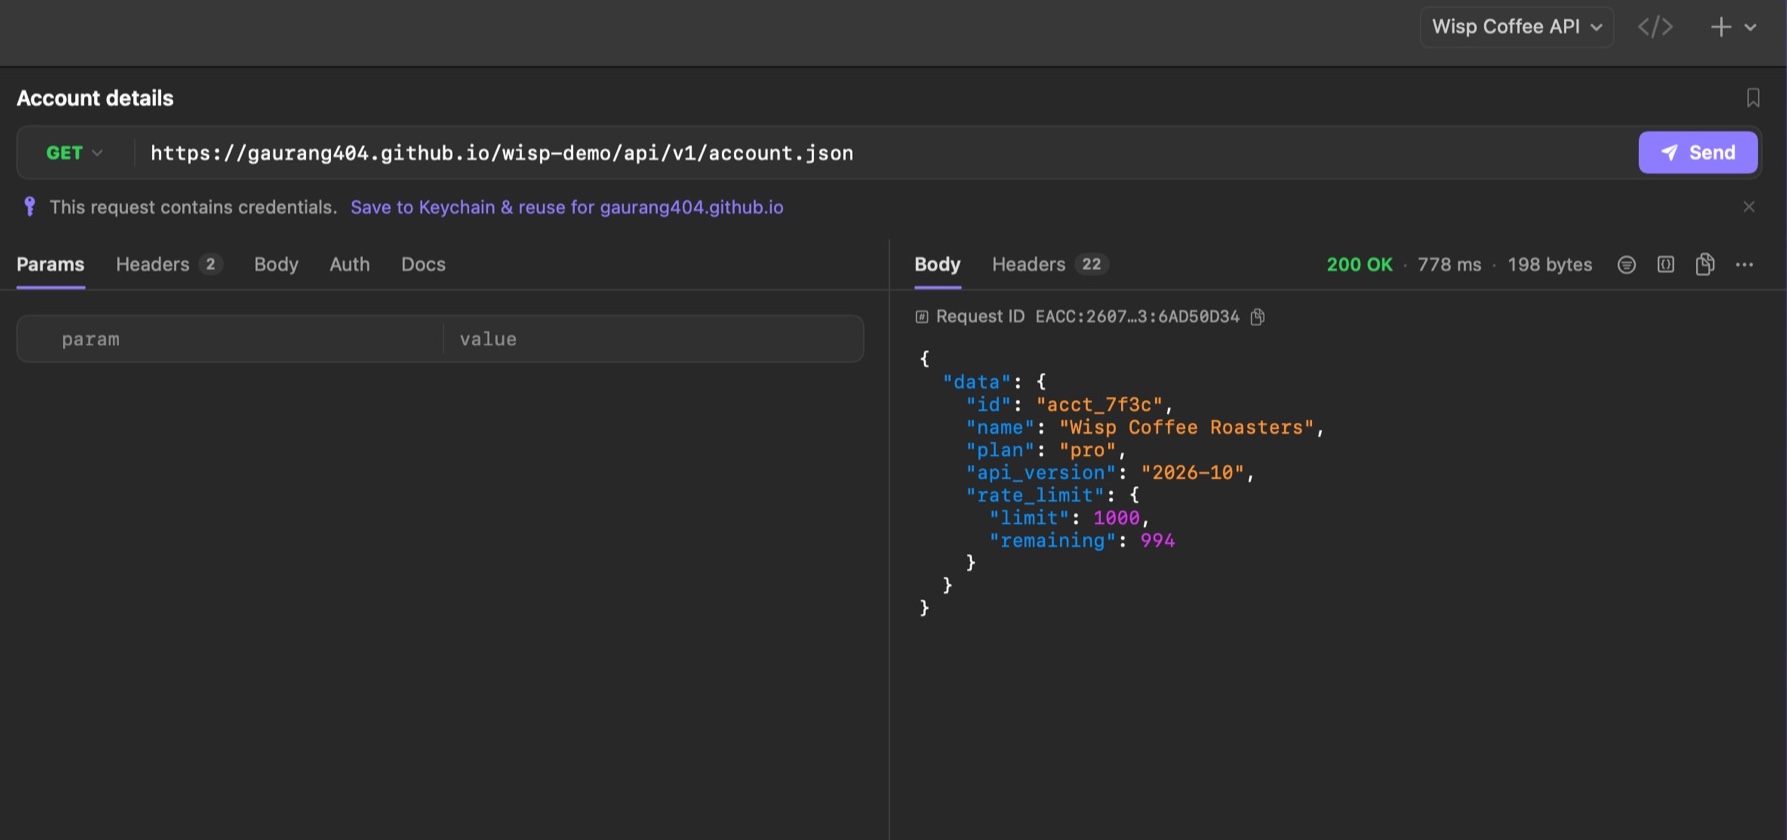
Paste a request that carries a token and Wisp spots it — Bearer, Basic, API-key headers, api_key in the URL. One click moves it into a Keychain-backed variable and scrubs it from your history.
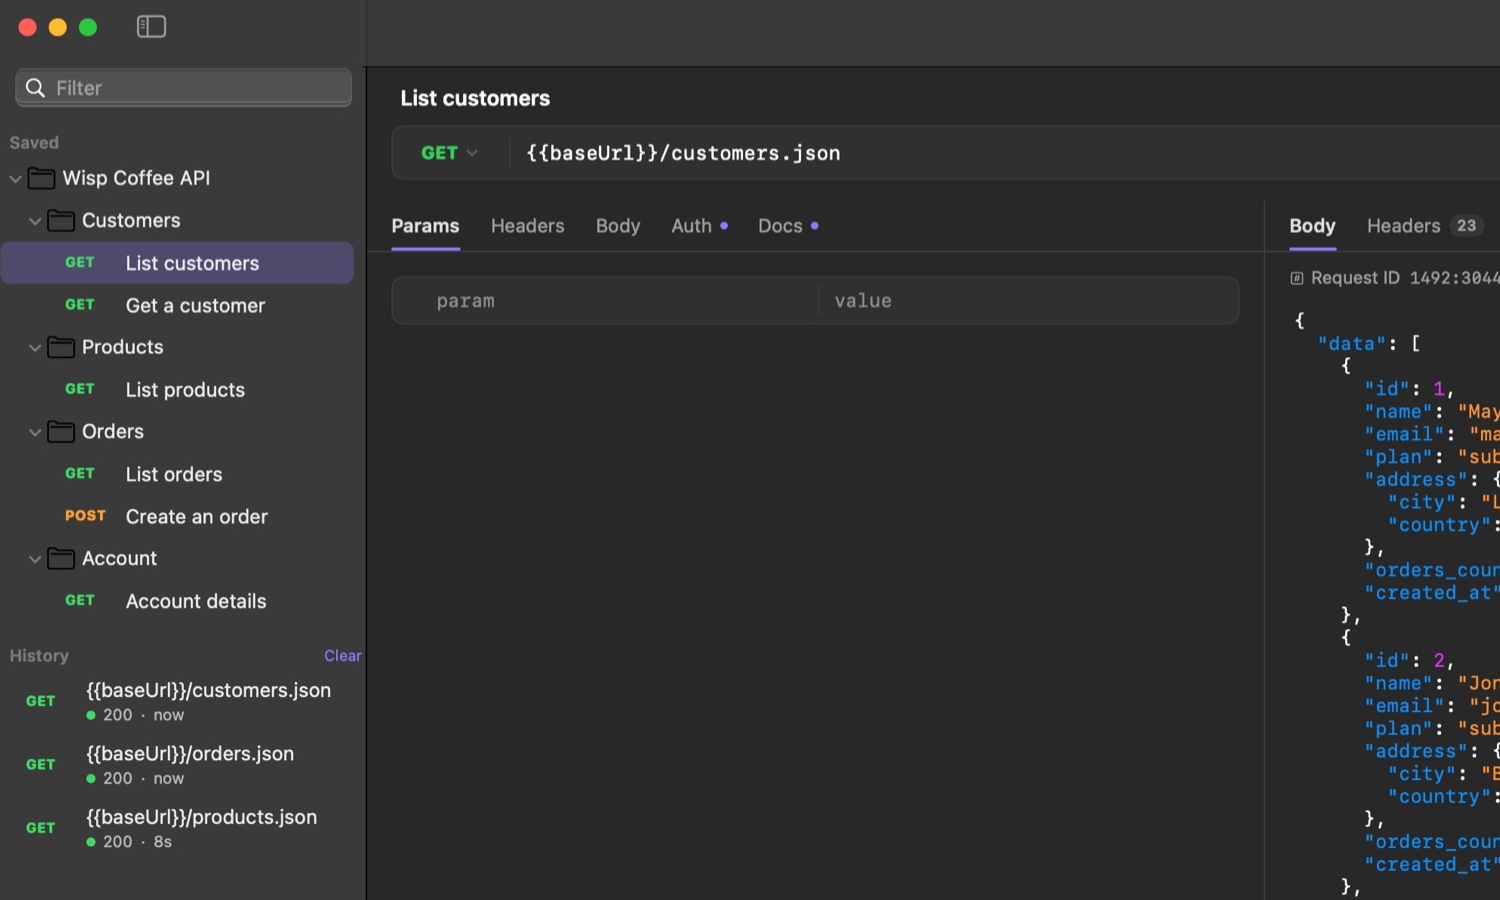
- One environment per API, picked automatically from the host
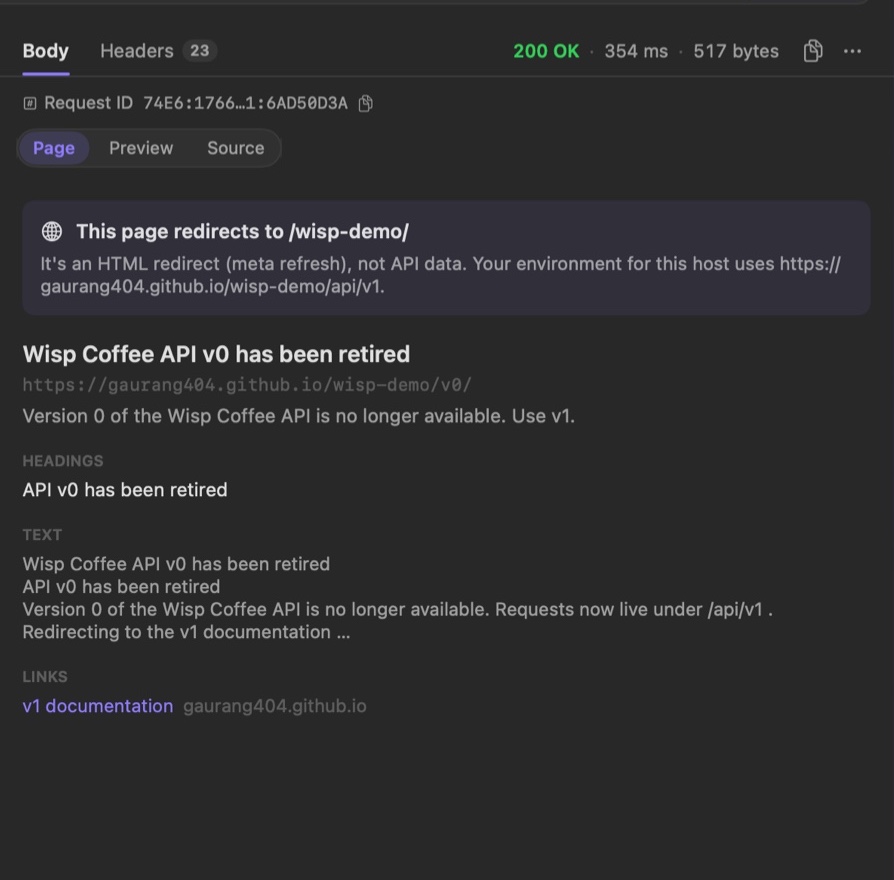
- Auth is never sent to another host — not even on redirects
- OAuth 2 with PKCE; tokens cached and refreshed for you